The automation project started with a tool trial and a Slack channel. Six months later there are 400 UI tests, nobody agrees which ones block a release, two of them fail every Tuesday, and the engineer who wrote the framework has moved teams.
None of that is a tooling problem. It's a missing document.
A test automation strategy document sets out what your team will automate, at which test layer, with which tools, in which environments, and how results gate releases. It also names who owns the suite, how flaky tests are handled, which KPIs you track and how tests are maintained, so automation stays trusted as the product changes.
Key takeaways
- An automation strategy is narrower than a test strategy: it decides what machines check, and how those checks gate delivery.
- Decide "automate vs keep manual" with explicit criteria, not enthusiasm.
- Write the flaky-test policy and ownership down before the suite grows. They're the sections that keep it alive.
- Keep it short. Two to five pages that people read beats thirty that nobody opens.
What is a test automation strategy document?
It's the agreement between engineering, QA and product about how automated testing works on your product. It answers practical questions: which tests run on a pull request, what blocks a merge, who fixes a broken test, and when a test should be deleted.
A general test strategy covers all testing, manual and automated, along with approach, scope and exit criteria. Our guide on how to write a test strategy document covers that wider document. The automation strategy sits inside it, or alongside it, and goes deeper on tooling, pipelines and maintenance.
A test plan is different again. A plan is for one release or project, with dates and names. The automation strategy changes rarely and applies to every release.
What sections should the document include?
Eleven sections cover what most teams need. Use the table as a checklist, then the template below for what to write in each.
| # | Section | The question it answers |
|---|---|---|
| 1 | Scope and goals | Why are we automating, and for which products? |
| 2 | Automate vs keep manual | Which tests should a machine run? |
| 3 | Test layers | How much at unit, API and UI level? |
| 4 | Tooling and framework | What do we build tests with, and why? |
| 5 | Environments and test data | Where do tests run, against what data? |
| 6 | CI/CD integration and gates | What runs when, and what blocks a release? |
| 7 | Flaky-test policy | What happens when a test is unreliable? |
| 8 | Ownership (RACI) | Who writes, reviews, fixes and decides? |
| 9 | Reporting and KPIs | How do we know it's working? |
| 10 | Maintenance | How do tests stay current? |
| 11 | Risks | What could derail this, and what's the plan? |
The test automation strategy template, section by section
Copy the headings into your document and answer the prompts under each. Delete prompts that don't apply rather than writing filler.
1. Scope and goals
State the products, platforms and teams covered, and what's out of scope. Then name two or three goals in measurable terms.
- Products and platforms in scope (web app, mobile, APIs, integrations)
- Explicitly out of scope (legacy admin tool, third-party portals)
- Goals, e.g. "full regression in under 30 minutes" or "no manual regression pass before weekly releases"
2. What to automate and what to keep manual
Write the criteria, not a list of tests. A test is a good automation candidate when it runs often, has a deterministic expected result, and covers a high-risk journey.
- Automate: smoke and regression checks, data-driven variations, API contracts, permission checks, cross-browser runs of core flows
- Keep manual: exploratory testing, usability and visual judgement, one-off checks, features still changing daily
- Decision rule: e.g. "automate once a manual case has run in three releases without changing"
Our post on software testing strategies explains how to score journeys by risk.
3. Test layers (the pyramid)
Mike Cohn's test pyramid, described in his book Succeeding with Agile and explained in The Practical Test Pyramid on Martin Fowler's site, gives two rules: write tests at different granularity, and the higher the level, the fewer tests you should have.
- Target split by layer (unit, API or service, UI end-to-end)
- Which layer owns which risk (business rules at API level; journeys at UI level)
- Rule for moving a check down a layer when it's slow or brittle
4. Tooling and framework
Record the choice and the reasoning, so it can be revisited without starting from scratch.
- Tools per layer, and who can use them (developers only, or QA and product too)
- Selection criteria: languages, platforms covered, CI support, maintenance cost, licence
- Framework conventions: naming, folder structure, locator strategy, reusable steps
- Exit plan: how tests could be exported or migrated
5. Environments and test data
Most automation failures are environment or data problems, so be specific.
- Which environment each suite runs against (ephemeral per pull request, shared staging, pre-production)
- How test data is created: seeded per run, created by the test, or reset nightly
- Rules for accounts, secrets and third-party sandboxes
- What never runs against production
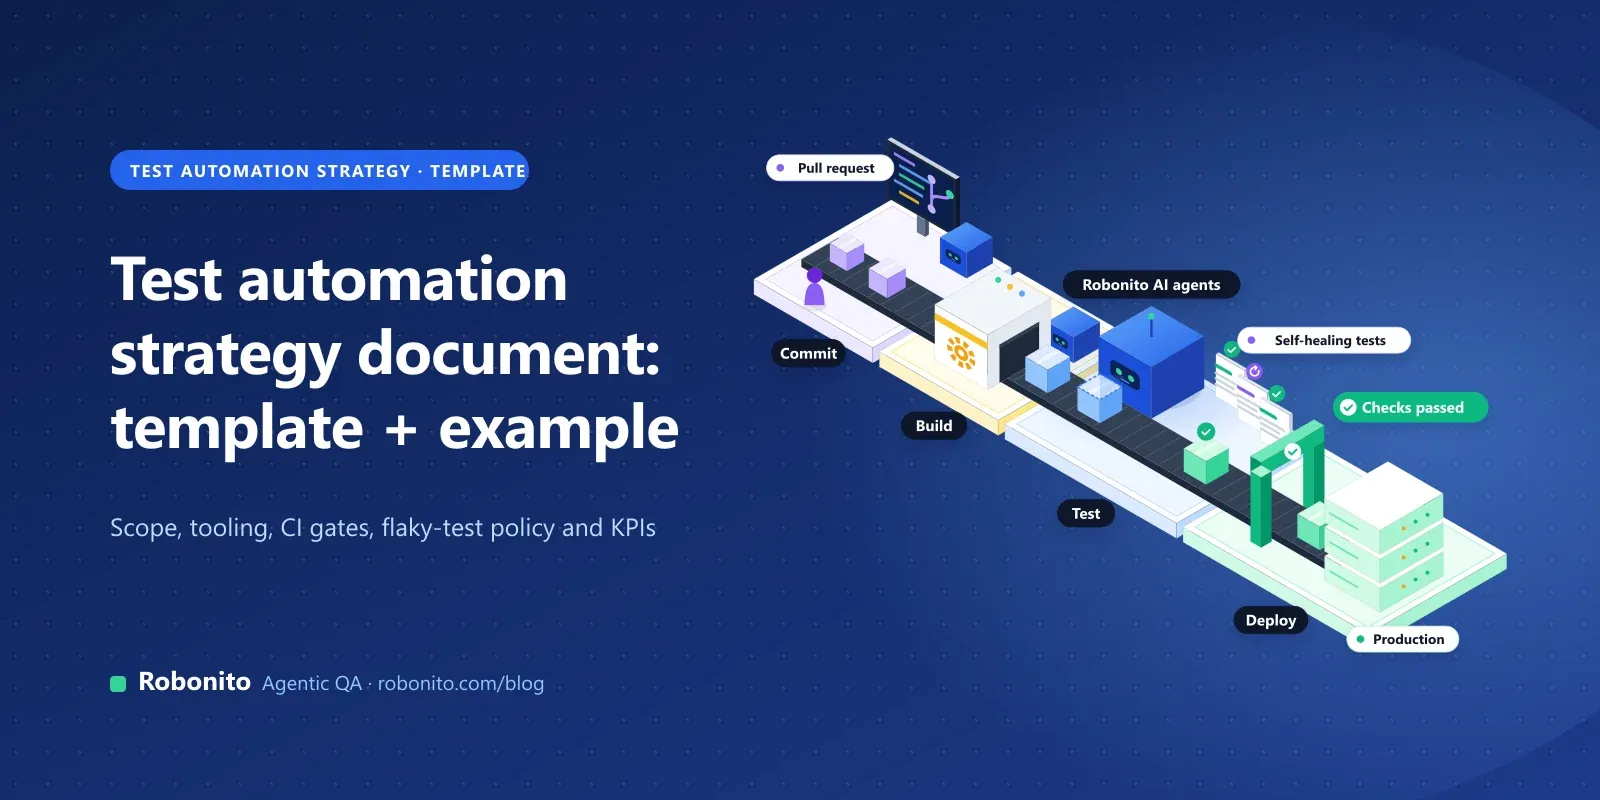
6. CI/CD integration and quality gates
Map suites to pipeline stages and say which results block.
| Stage | Suite | Blocks? |
|---|---|---|
| Pull request | Unit, API, UI smoke | Yes, merge |
| Merge to main | Full regression, in parallel | Yes, deploy to staging |
| Nightly | Long journeys, extra browsers | No, but triaged next morning |
| Pre-release | Release candidate run | Yes, release |
If you use GitHub, required status checks on a protected branch enforce the first gate: all required checks must pass before changes can be merged.
7. Flaky-test policy
A flaky test passes and fails on the same code. Playwright's retries documentation uses a useful definition: tests that failed on the first run but passed when retried.
- How flakiness is detected (retry reports, failure history)
- Quarantine rule: e.g. "a test that flakes twice in a week leaves the blocking suite within a day"
- Fix-or-delete deadline for quarantined tests
- Retry limits, so retries don't hide real defects
8. Ownership and RACI
Name roles, not people, so the document survives reorganisations.
| Activity | Responsible | Accountable | Consulted | Informed |
|---|---|---|---|---|
| Write tests for new features | Feature developer or QA | Engineering lead | Product | Team |
| Review test changes | QA lead | QA lead | Developers | Team |
| Fix a broken test | Whoever broke it | Engineering lead | QA | Team |
| Change gates or tools | QA lead | Head of engineering | Developers | Product |
9. Reporting and KPIs
Pick a handful of measures and say where they're shown.
- Time to feedback on a pull request and on a full run
- Flake rate and size of the quarantine list
- Escaped defects: regressions found after release
- Coverage of top-risk journeys, not raw test count
- Optional delivery metrics, such as DORA's change fail rate and change lead time
10. Maintenance
Tests are code (or configuration) and decay like code.
- Definition of done includes updating affected tests
- Regular review to delete duplicate or low-value tests
- Locator and step conventions that survive UI changes
- Budget: who spends time on suite health, and how often
11. Risks and mitigations
List the risks you can already see: a single framework expert, unstable staging, test data tied to one shared account, licence costs at scale. For each, give a mitigation and an owner.
How do you write an API automation test strategy?
API tests deserve their own subsection, because they're faster and more stable than UI tests and catch most business-rule defects. Add these points under sections 3 to 6.
- Source of truth. Name the API description you test against, such as an OpenAPI definition (a standard, language-agnostic interface description for HTTP APIs), and keep it versioned with the code.
- Contract tests. For services owned by different teams, consider consumer-driven contracts. Pact describes itself as a code-first consumer-driven contract testing tool; the consumer's expectations run in the provider's pipeline.
- Functional and negative cases. Status codes, schemas, validation errors, authorisation per role, pagination and idempotency.
- Data. Create and tear down records through the API itself, and isolate each test's data.
- Running in CI. If your team uses Postman collections, note the runner. Postman describes Newman as its command-line collection runner, but says it won't receive updates and recommends the Postman CLI for CI.
- Performance thresholds. Load tools can gate too. In k6, a failed threshold such as
p(95)<200on request duration makes k6 exit with a non-zero code, which fails the pipeline step.
Example: a filled-in automation strategy for a SaaS team
This is a fictional example to show the level of detail. The company, team and targets are invented.
Ledgerly sells invoicing software to small businesses: a web app, a public REST API and a payments integration. The team is ten developers, two QA engineers and one product manager, releasing weekly.
1. Scope and goals. In scope: web app, public API, payment webhooks. Out of scope: the internal back-office tool. Goals: replace the two-day manual regression pass; full regression under 30 minutes; every P1 journey automated within two quarters.
2. Automate vs manual. Automate login, invoice creation, sending, payment and refunds, plus role permissions. Keep manual: new-feature exploratory sessions and PDF layout review. A case is automated after three unchanged releases.
3. Layers. Business rules (tax, currency rounding, due dates) are tested at unit and API level. UI tests cover eight end-to-end journeys only.
4. Tooling. Unit tests in the language's standard framework; API tests from the OpenAPI definition; UI journeys in a tool QA and product can both edit. Criteria recorded: CI support, maintenance effort, export options.
5. Environments and data. Pull requests get an ephemeral environment with seeded data. Payments use the provider's sandbox. Nothing runs against production except a read-only synthetic login check.
6. Gates. PR: unit, API and four UI smoke journeys must pass to merge. Main: full regression in parallel must pass to deploy to staging. Friday release candidate run must pass to release.
7. Flaky tests. Two flakes in seven days moves a test to quarantine. Quarantined tests are fixed or deleted within ten working days. One retry maximum.
8. Ownership. Whoever breaks a test fixes it. The QA lead approves gate and tool changes.
9. KPIs. PR feedback time, full-run time, flake rate, escaped regressions per month, P1 journey coverage. Shown on the team dashboard and reviewed at each retro.
10. Maintenance. "Tests updated" is in the definition of done. Monthly 30-minute review to delete or merge low-value tests.
11. Risks. One engineer knows the API test harness (mitigation: pair on it this quarter). Shared payment sandbox can rate-limit (mitigation: mock it in PR runs, use the real sandbox nightly).
That's the whole document: about two pages. For the regression side in more depth, see our guide to automated regression testing.
What mistakes make automation strategies fail?
- Counting tests instead of risk covered. Hundreds of tests can still miss checkout.
- No flaky-test rule. Teams start ignoring red builds within weeks.
- One owner. When the framework author leaves, the suite stalls.
- Gates nobody enforces. If a failing suite doesn't block anything, it's a report, not a gate.
Where Robonito fits, and where it doesn't
Robonito is an agentic QA platform where AI agents create, run and maintain end-to-end tests. It maps onto several sections of the template.
- Tooling (4). Build tests in plain text, by recording in the desktop app, or from reusable no-code steps, with low-code extensions for edge cases. Robonito can also generate executable code for test cases, which helps the exit plan.
- API strategy. AI Studio can generate tests from Swagger/OpenAPI definitions, and you can import Postman collections. API testing is on Pro and Enterprise.
- CI gates (6). Suites run from Jenkins, GitHub Actions, GitLab CI or Azure DevOps on Starter and above, in parallel isolated cloud workers. Local runs on your own CI runners are free on every plan.
- Flaky tests and maintenance (7, 10). Self-healing adapts steps when labels, layouts or locators change and logs each healed step for review.
- Reporting (9). Every run keeps video, network traces and an AI root cause for failures, with pass rates, trends and risk analysis across runs.
Where it doesn't fit: Robonito doesn't replace unit tests or developer-owned contract tests, and it won't write your strategy. The decisions in sections 1, 2, 8 and 11 are yours.
See how suites plug into your pipeline on the CI/CD test automation page, or to walk through your draft strategy.
Frequently asked questions
What is a test automation strategy document?
A short document that defines what a team automates, at which test layer, with which tools and environments, and how automated results gate merges and releases. It also covers flaky-test handling, ownership, KPIs and maintenance, so the suite stays reliable as the product and team change.
How is an automation test strategy different from a test plan?
The strategy is long-lived and applies to every release: principles, layers, tools, gates and ownership. A test plan covers one release or project, with scope, dates, people and specific test cycles. Most teams keep one automation strategy and write a lighter plan per release that refers to it.
How long should a test automation strategy document be?
Usually two to five pages. It should be short enough that new team members read it in one sitting. Put detail that changes often, such as tool configuration or test lists, in linked pages or the repository, and keep the strategy to decisions and rules.
What should an API automation test strategy include?
The API description you test against, the split between functional, negative and contract tests, how test data is created and cleaned up, authorisation checks per role, how tests run in CI and which failures block, and any performance thresholds. Keep business-rule checks at API level rather than UI level.
Who should own the test automation strategy?
Usually the QA lead or the engineering lead, with input from developers and product. Ownership of the document is different from ownership of the tests: the strategy should say who writes, reviews and fixes tests, ideally the people whose changes break them.
Ready to put your strategy into a pipeline? , or and wire your first suite into CI.